- Filter and Query Logs
- Copy Log Meta Data as JSON
- Share Log
- View What Happened Here
- Time Detective
- View Live Trail
Filter and Query Logs
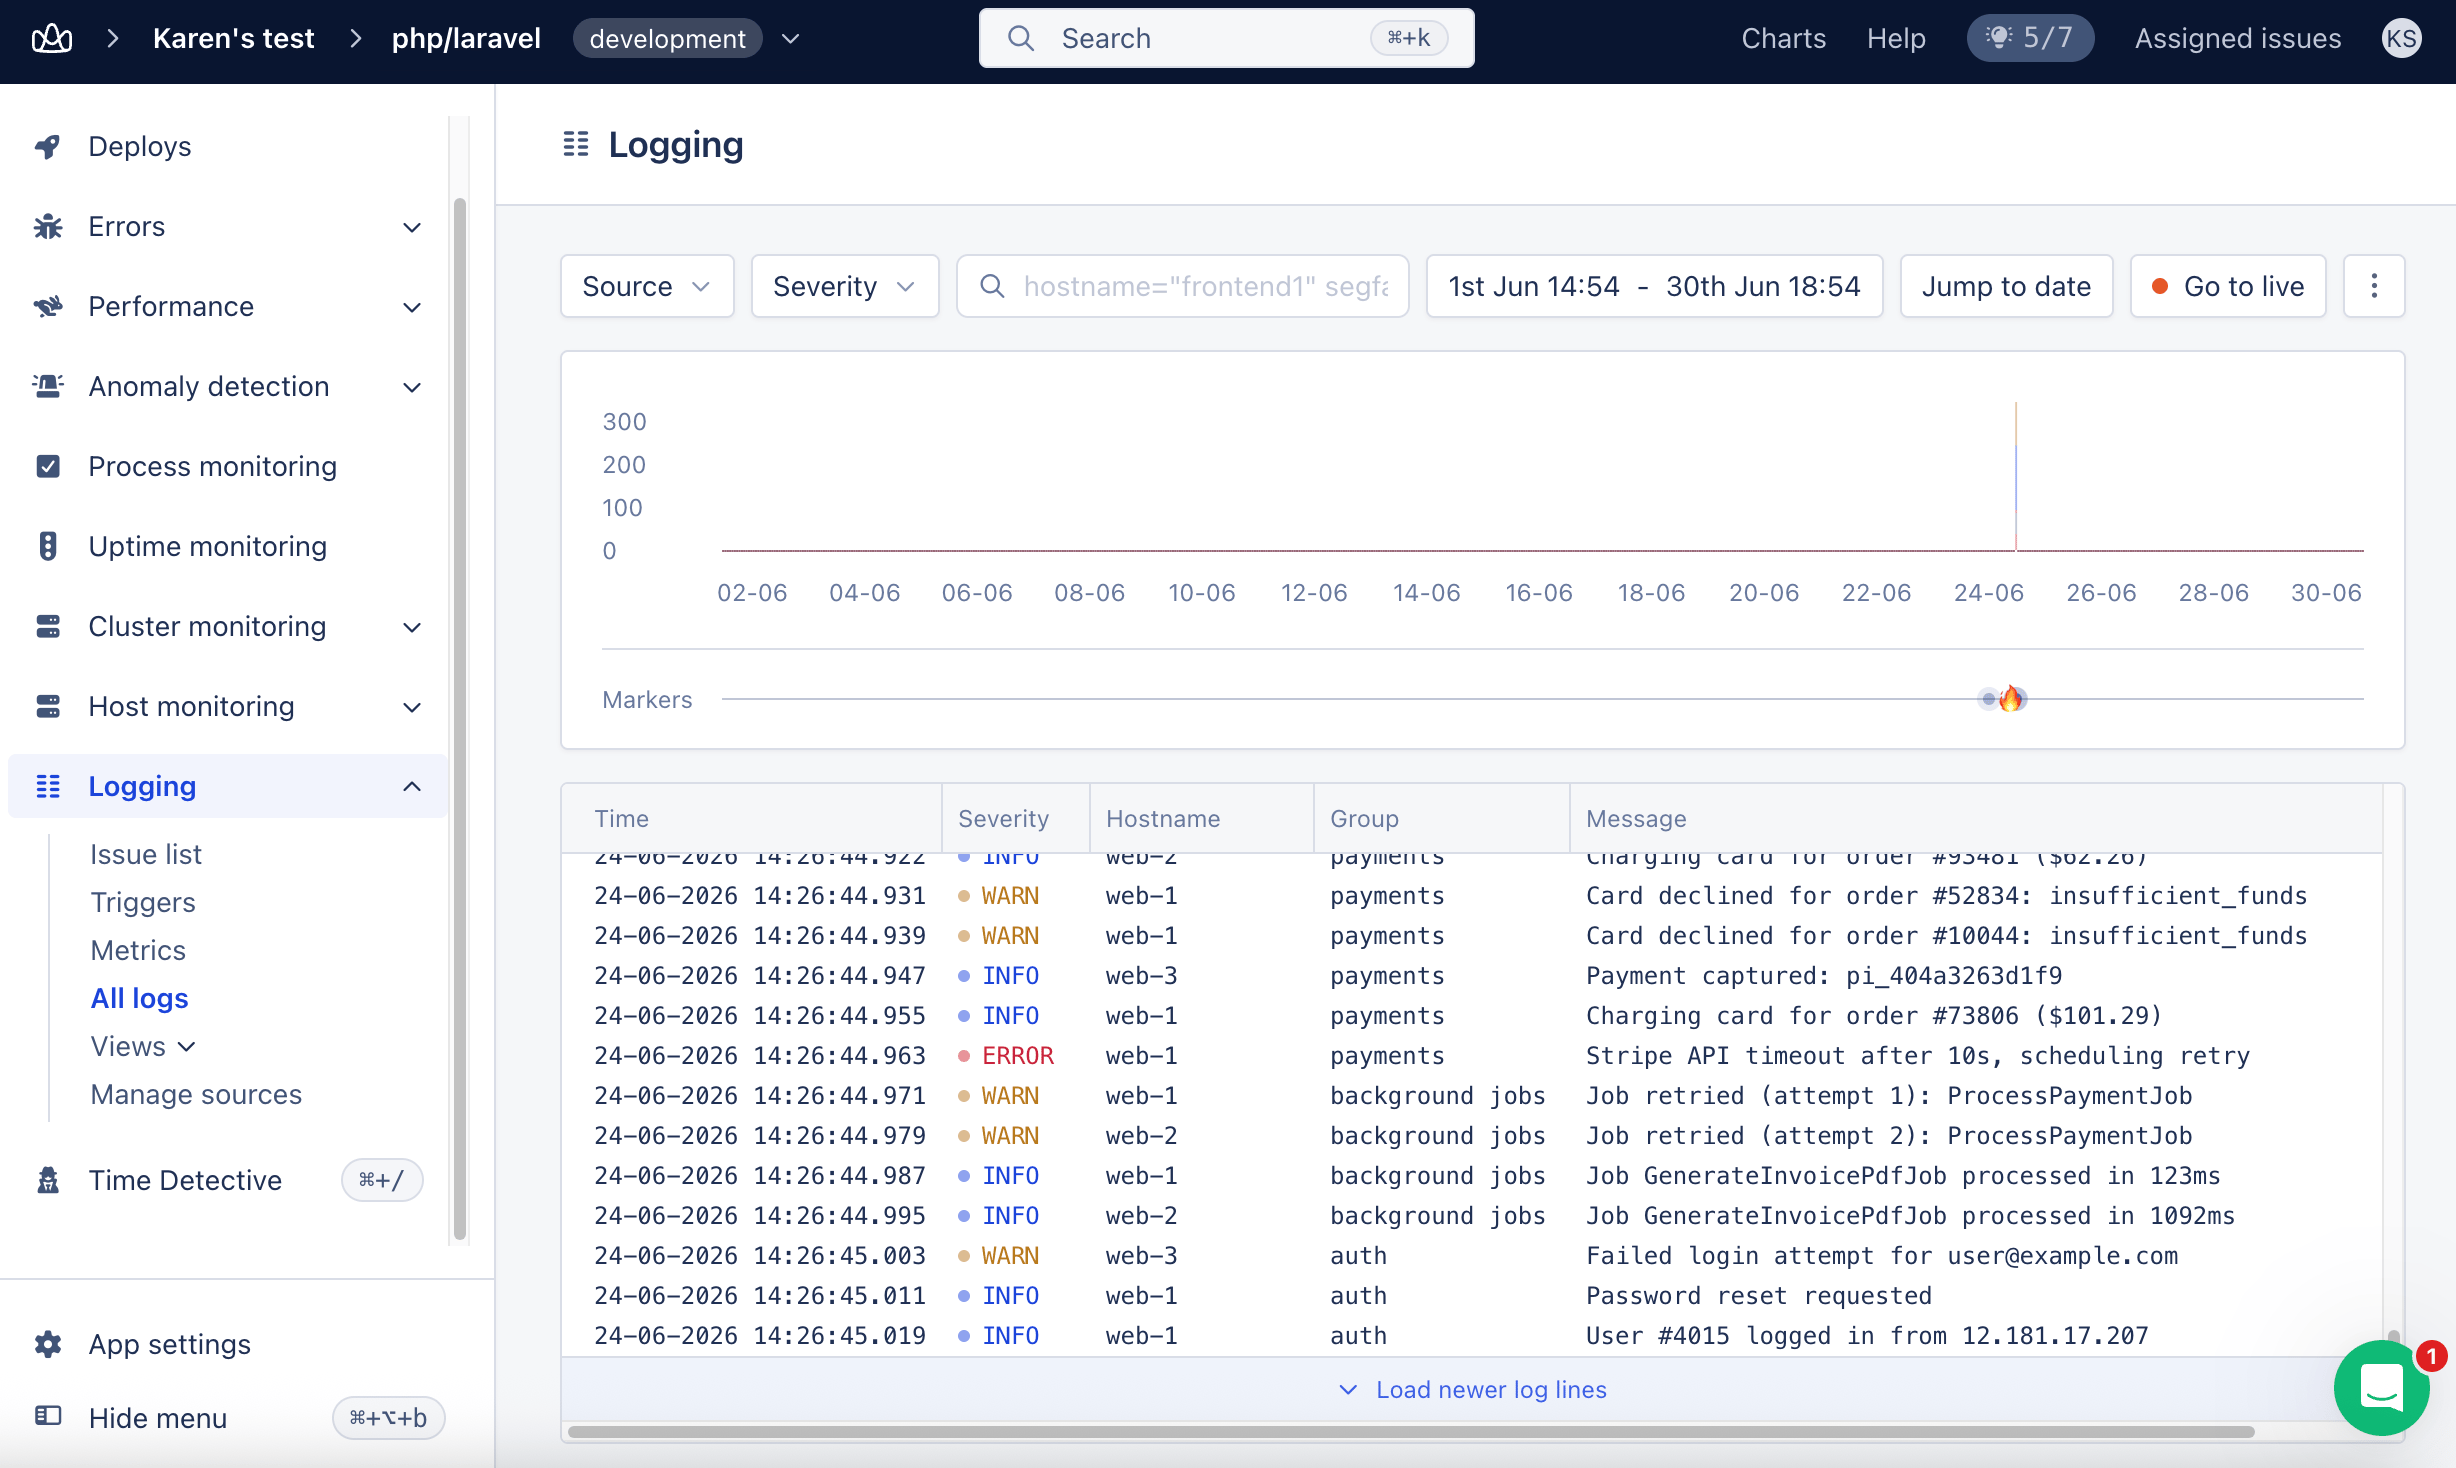
Use the “Source” drop down to filter which sources you see the logs for. Use the “Severity” drop down to filter the severity of logs Filtering and querying are further explained in the Query Syntax section of this guide.Copy Log Meta Data As JSON
Expand a log by pressing the ”+” button, click “Copy as JSON”. Meta data will automatically be copied to your clipboard as a valid JSON object.Share Log
Click “Copy link to log line” and a link to this log line will automatically be copied to your clipboard.What Happened Here
Want to see a snapshot of your application’s metric at the exact time the log line was written? Click “What Happened Here”Time Detective
Use the “Time Detective” button to investigate application wide data at the time a log line was written. Time Detective shows the minute or the hour that contains the moment you selected, depending on how long ago that moment was:- Within the last 48 hours: a 1-minute window, from the start of the selected minute.
- Older than 48 hours: a 1-hour window, from the start of the selected hour.
Live Trail
Clicking “Go to live” will take you to a live trail of your logs.Managing Sources
To modify a source go to AppSignal > Logging > Sources and click “Manage source”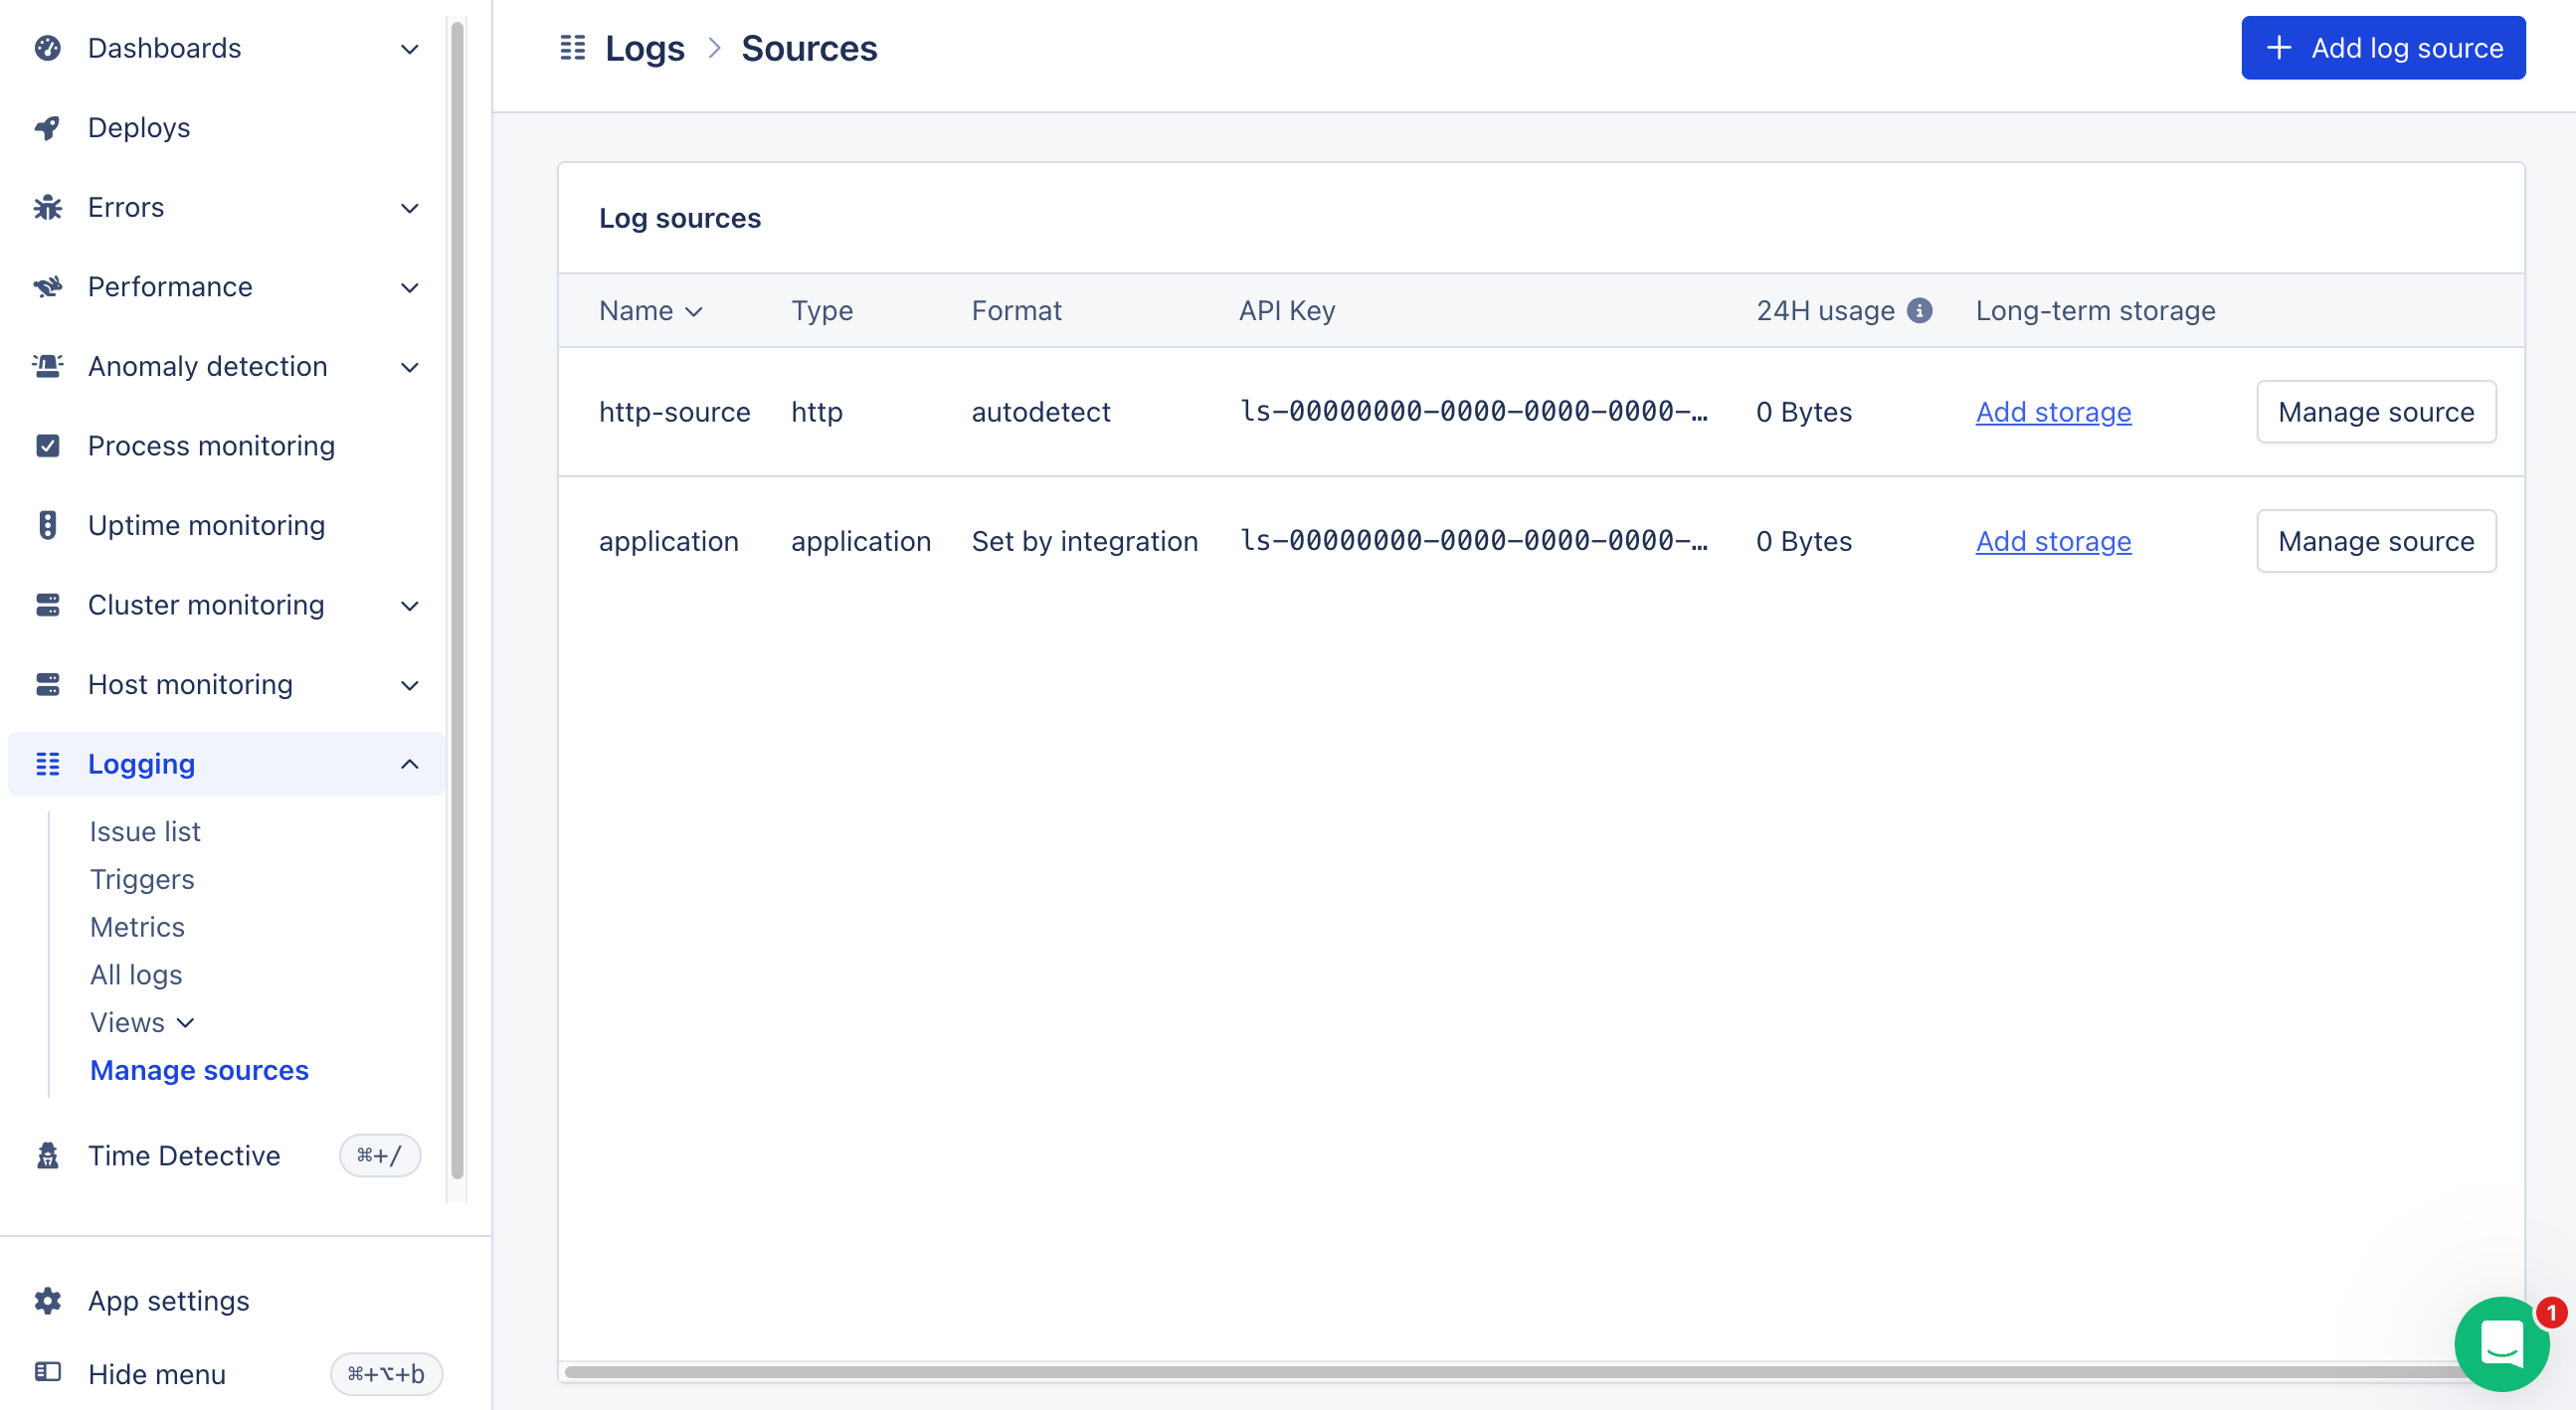
Edit Source
To edit the source click “Edit source” in the top right corner of the screen. You can edit the following source attributes:- Name
- Platform (currently limited to syslog)
- Format
Remove Source
Deletion is permanent and will revoke the API key used for that source. Before removing a log source, we recommend ensuring that the source is no longer sending logs to AppSignal so that your application is not making unnecessary calls to third parties. Before removing the log source in AppSignal, remove the rsyslog configuration file for this log source (located inetc/rsyslog.d) and restart rsyslog with the below command.
Bash